
Delivering enterprise-grade security, privacy and compliance
Our conversational AI platform gives you the controls to protect your users and data, keep your system safe, and meet compliance requirements.
Supports global standards and regulatory obligations
Certified, audited and compliant with security, privacy and AI standards, and service provider regulatory obligations.
Compliant, audited and certified
Information Security Management System (ISMS).
Compliant, audited and certified
Privacy Information Management System (PIMS).
Compliant
Artificial intelligence management system.
Compliant and audited
Annual audit of security, availability and confidentiality controls.
Compliant
Assurance standard for organizational controls.
Compliant
Assurance standard for organizational controls.
Accredited
Financial Services Qualification System, used for supplier due diligence in financial services.
Compliant
Card data is processed by a sub-processor that is compliant, audited and certified.
HIPAA
Compliant and audited
US rules for the privacy and security of health information.
Aligned
Our development follows Open Web Application Security Project best practices.
Aligned
Web Content Accessibility Guidelines.
Compliant
Other regulation, including GDPR, EU AI Act and DORA.
Defense in depth, by default
Security and privacy controls are built into how the platform is designed and operated.
-
Encryption everywhere
TLS 1.2+ in transit, AES-256 at rest. Per-tenant key isolation across the platform.
-
Granular access control
SSO via SAML/OIDC, role-based permissions, audit logging on every privileged action.
-
Privacy by design
Configurable data retention, PII redaction, and data-processing agreements available on request.
-
24/7 monitoring
Continuous monitoring, automated threat detection, and an established incident-response program.
-
EU data residency
Customer data hosted in EU regions by default, so no cross-border transfers are required.
Protection built into the platform
boost.ai’s conversational AI includes robust and adjustable security and privacy protection mechanisms, such as:
Data protection
- Segregated single-tenant customer environments
- Data encryption at transfer and at rest
- Anonymization and partial masking of data
Access control
- Password quality checks, 2-factor authentication
- Single Sign On (SSO)
- Role segregation
- IP allowlisting
Threat protection
- Malware detection
- Intrusion detection
- Distributed Denial of Service (DDoS) protection
- Hardening of servers to reduce attack surface
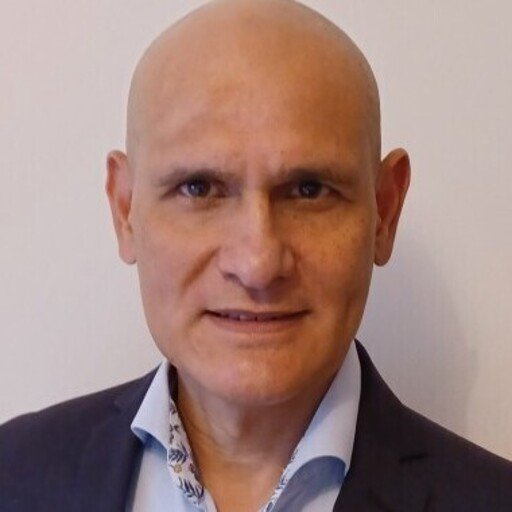
“Security and compliance is a key part of who we are and what we deliver. Our goal has always been to make the best solution for enterprises and to do that you also have to be best in class on security and compliance.”
Neil Oschlag-Michael
Head of AI Risk & Security
Compliance programs behind the platform
boost.ai’s compliance programs are based on industry best practices from globally recognized standards, such as:
- Access control
- Asset management
- Audits
- Availability zones
- Business continuity
- Communication security
- Cryptographic controls
- Development security
- Device management
- Disaster recovery
- Incident management
- Log and event tracking
- Mandatory security policies
- Operations security
- Patch management
- Penetration testing
- Physical security
- Privacy management
- Risk management
- Screening
- Security awareness training
- Vulnerability monitoring
Need the documentation?
Our live trust center has our security, compliance and data privacy documentation.